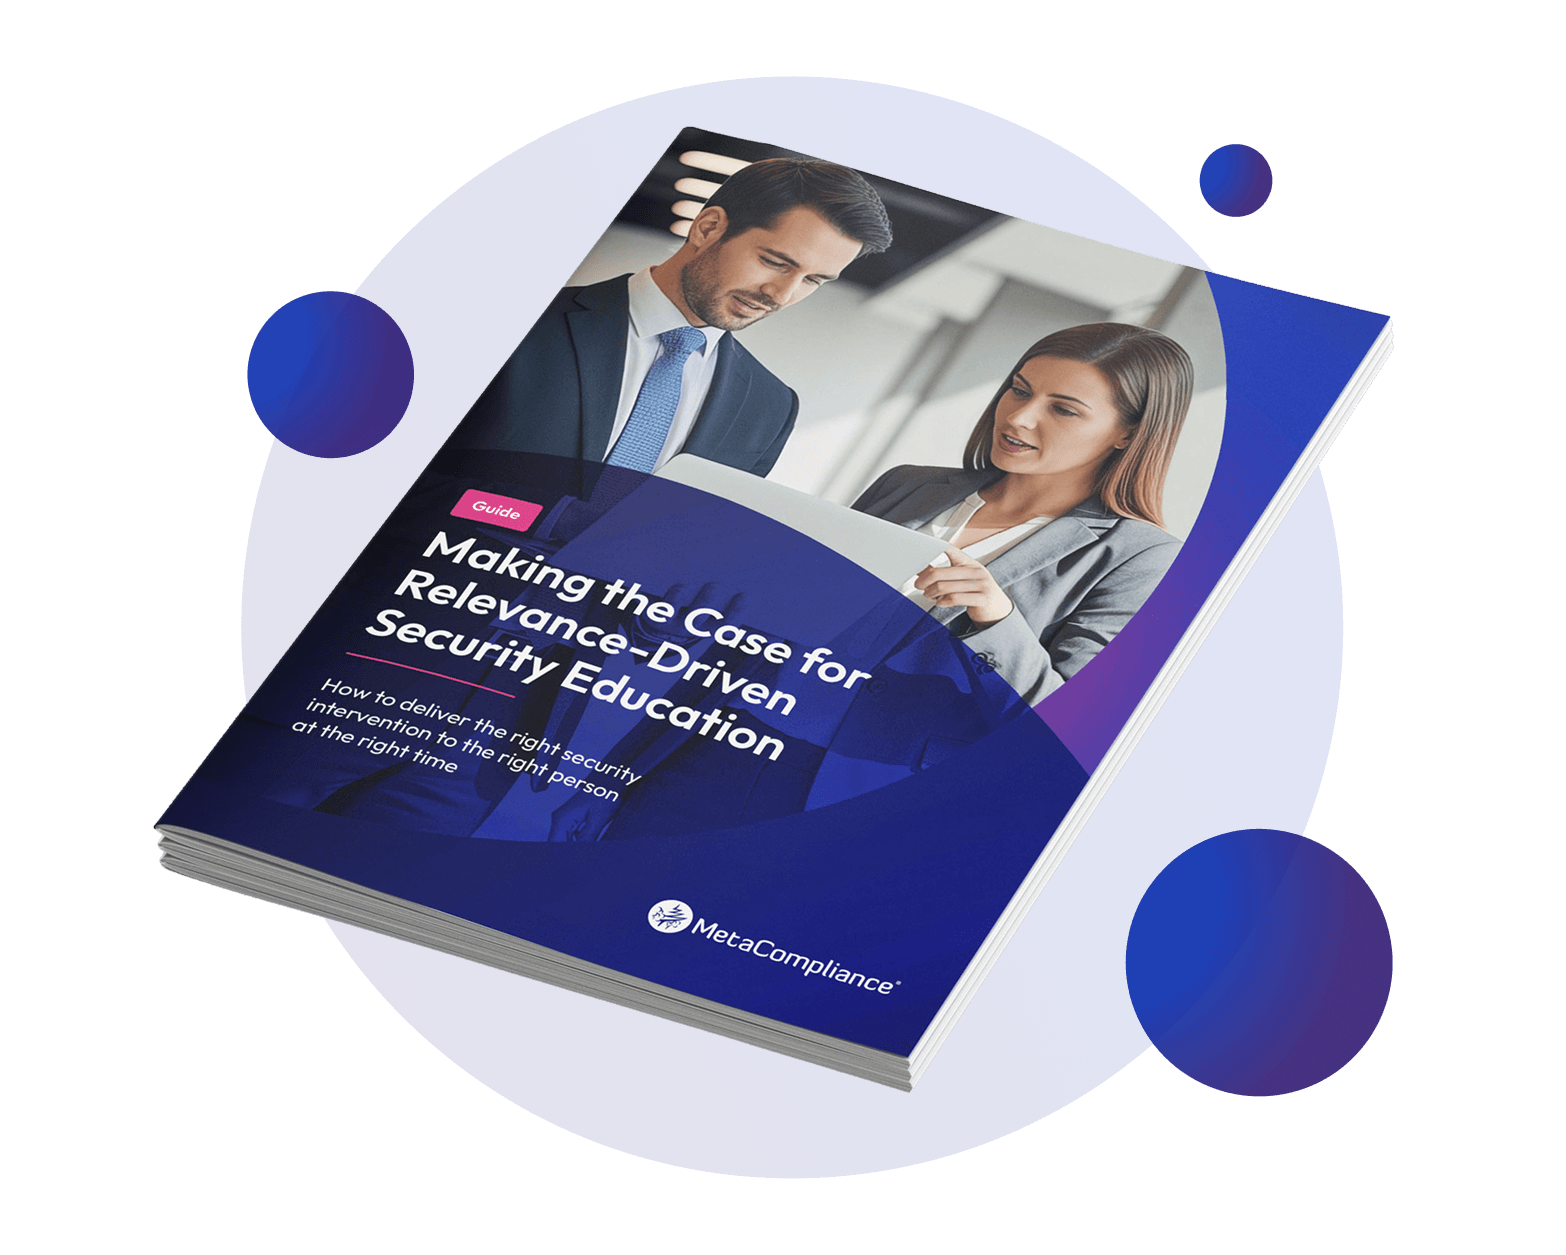
Relevance-Driven Security Education
Make Every Security Intervention Count
Security awareness programmes are busier than ever. Most employees are receiving training, phishing simulations and security communications consistently throughout the year, but more activity doesn’t necessarily mean less risk.
Our Rethinking Human Cyber Risk research found that 81% of CISOs believe security awareness training fails because it’s too generic to feel personally relevant, while three-quarters say relevance matters more than frequency when it comes to driving secure behaviour.
Risk isn’t the same for everyone. The threats faced by someone in finance can look very different from those targeting HR, IT or senior leadership. Even employees in the same role can demonstrate very different behaviours and levels of risk.
This guide explores how organisations can move beyond blanket security awareness campaigns and use role, risk and behavioural signals to make education more targeted, timely and effective.


Why relevance matters more than frequency when delivering security awareness training

How role, risk and behavioural signals can help determine which employee needs what security intervention, and when

How behaviour-triggered interventions can turn moments of risk into opportunities for relevant learning

How MetaCompliance helps organisations deliver targeted security education and continually adapt their approach
Who This Guide Is For
This guide is designed for security leaders looking to make their security awareness programmes more targeted, measurable and responsive to human risk.
It’s particularly valuable for:
- CISOs and security leaders responsible for reducing human cyber risk
- Security awareness professionals looking to move beyond blanket training campaigns
- Risk and compliance teams seeking a more targeted approach to employee education
- IT and cyber security teams using phishing and behavioural data to understand employee risk
- Senior stakeholders looking for clearer evidence that security awareness investment is making a difference
Whether you’re evolving an established security awareness programme or starting to take a more risk-driven approach to employee education, this guide provides a practical framework for making relevance part of your strategy.
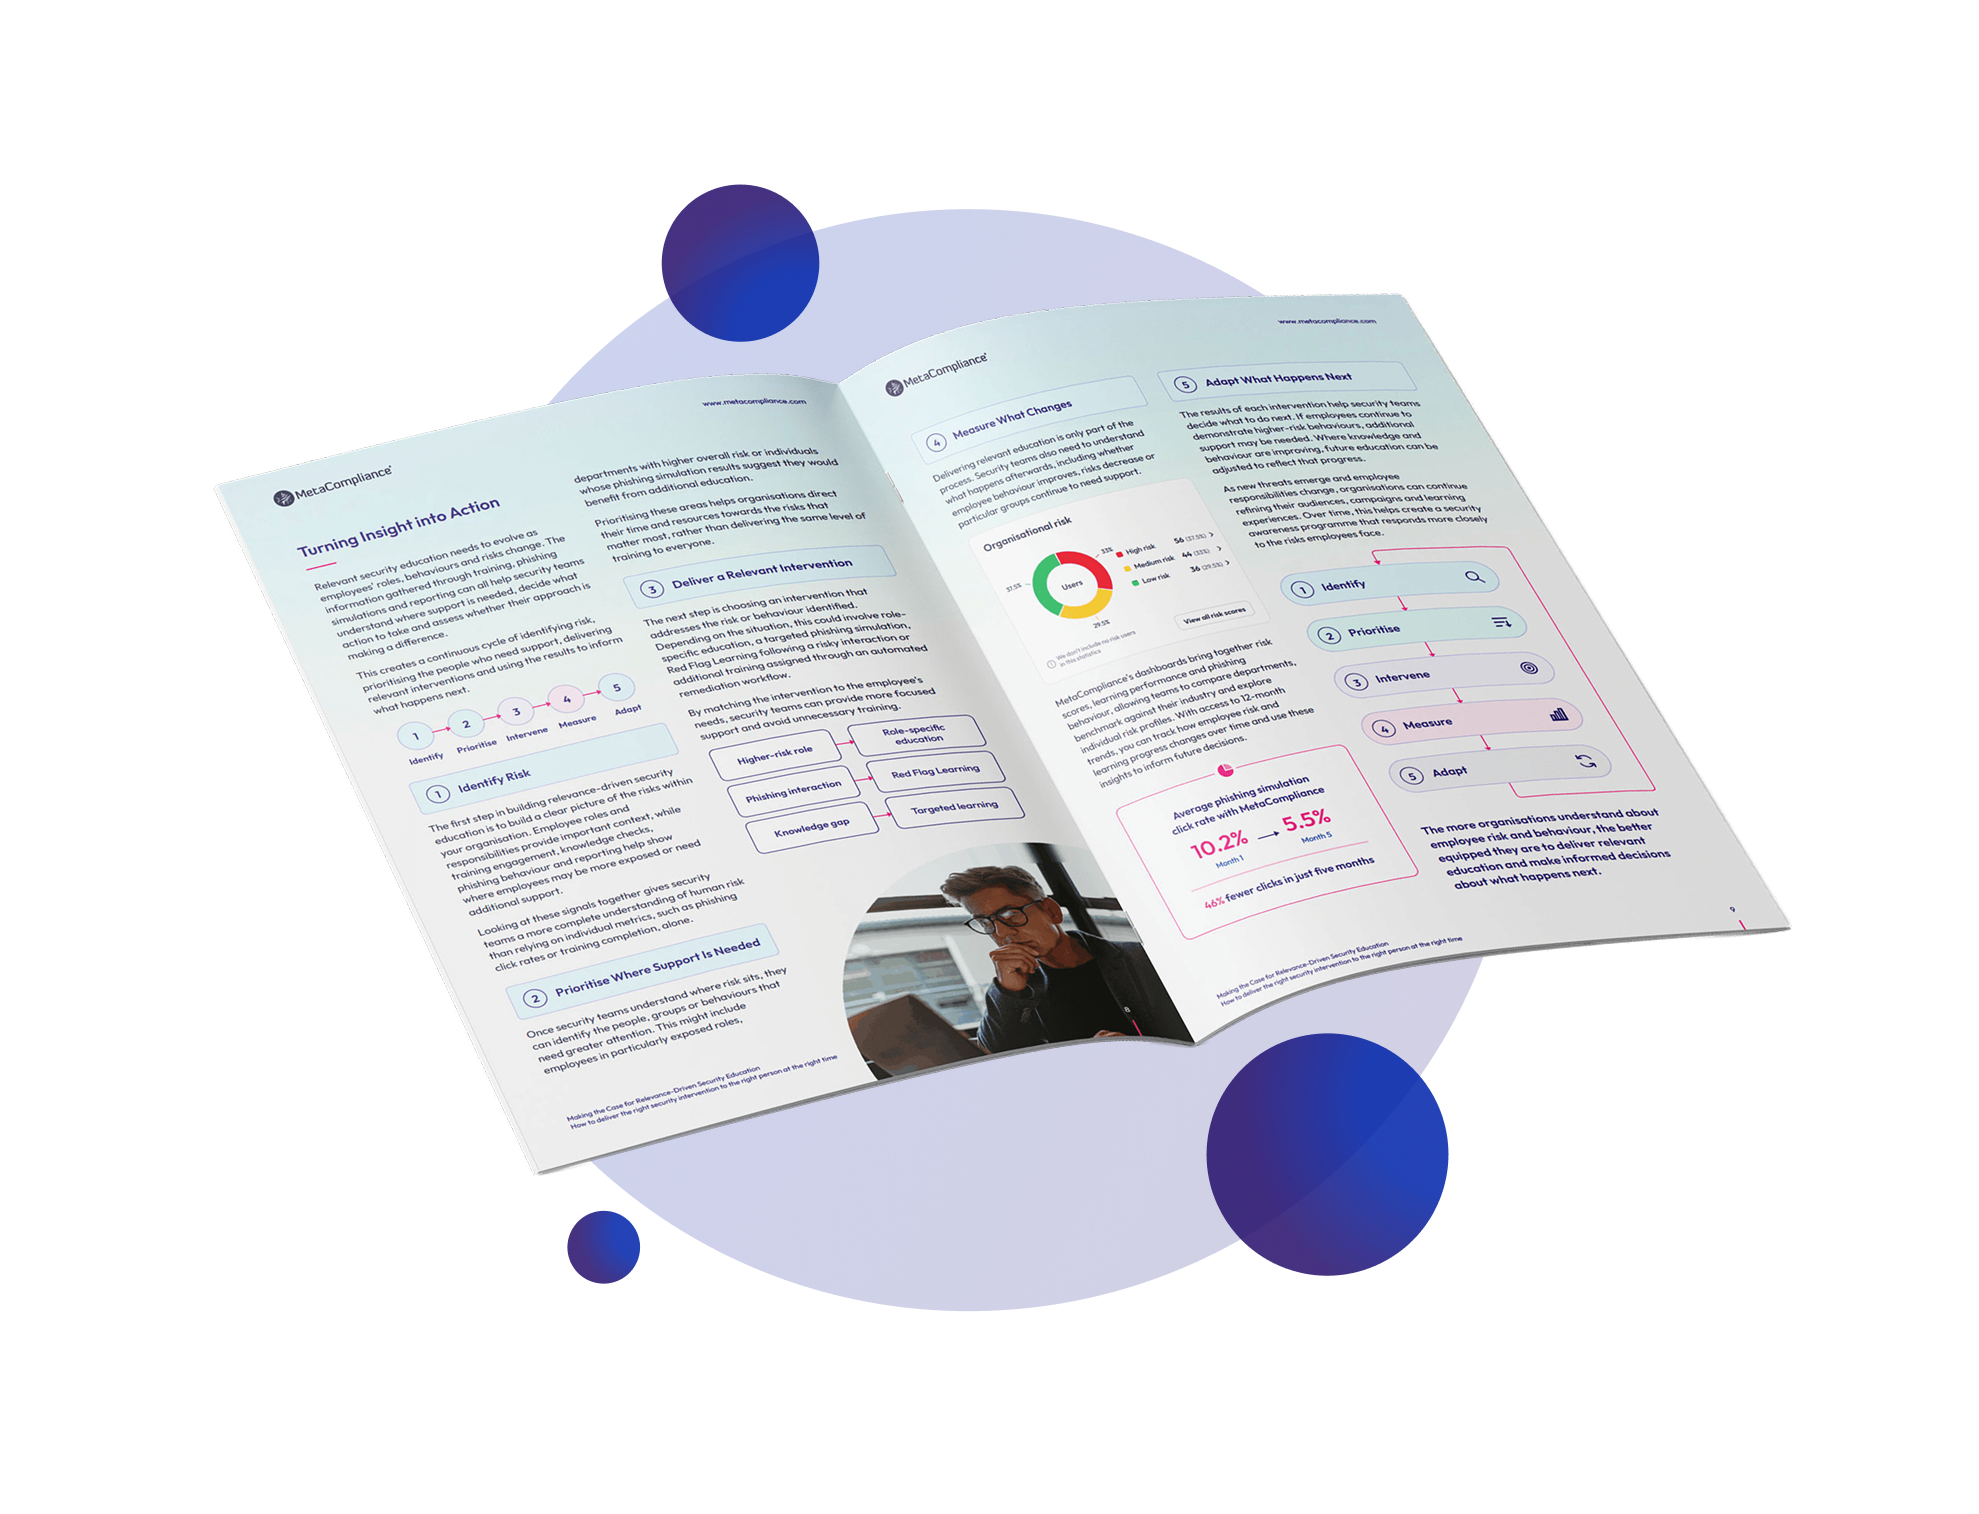

Make Relevance Part of Your Human Risk Strategy
The answer to human cyber risk isn’t simply more training. It’s making better decisions about who needs support, what intervention they need and when it will have the greatest impact.
MetaCompliance helps organisations identify human risk and turn those insights into more relevant, targeted security education, helping security teams focus their efforts where they matter most.
See how MetaCompliance can help you build a more relevance-driven approach to human cyber risk.